HKMA Issues Credit Card Security Warning After Mass Alleged Fraud Targeting iPhone Pre-orders
HK01 · 3 SOURCES1 day ago2 MIN
Summary
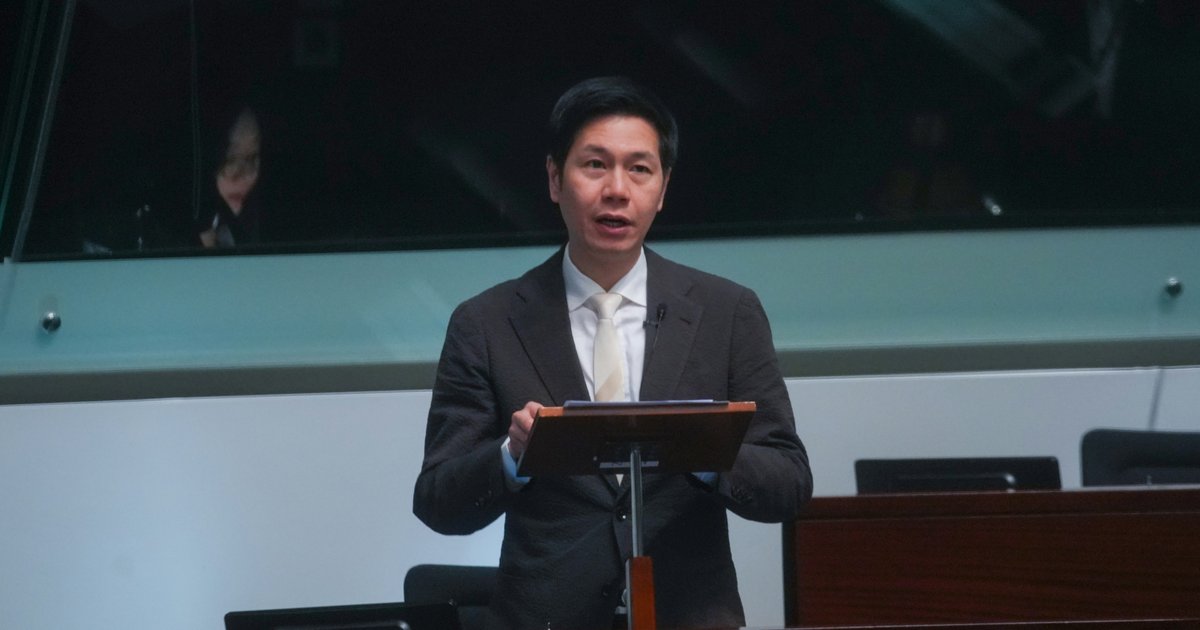
The Hong Kong Monetary Authority (HKMA) has issued a security reminder to credit card holders following widespread reports of suspected credit card fraud during iPhone pre-orders. Social media saw numerous complaints from customers claiming their credit cards were allegedly used to purchase iPhones without authorization. HSBC, one of the affected banks, confirmed it would assist customers with investigations and chargeback procedures. Legislative Council member Ng Kit-chong commented on the security standards merchants should maintain.
Key Points
- Over 700 individuals have reported suspected credit card theft used to purchase iPhone models that began pre-orders on Saturday
- HSBC stated it will investigate unauthorized transactions and initiate chargebacks in applicable cases under credit card organization rules
- The HKMA confirmed cardholders are not liable for unauthorized transactions if they committed no fraud or gross negligence
- Merchants who disable additional authentication such as one-time passwords or in-app verification must bear responsibility for losses
- LegCo member Ng Kit-chong said 3D Secure verification typically takes 30-40 seconds and merchants who disabled it prioritized customer experience over security
Why It Matters
This incident highlights the tension between merchant checkout convenience and transaction security in Hong Kong's e-commerce ecosystem. With the HKMA explicitly stating merchants bear liability when they disable security measures, this could set a precedent for consumer protection in unauthorized credit card transactions. The case underscores the need for companies holding large customer databases to strengthen their cybersecurity infrastructure as digital payments become increasingly prevalent.
This incident highlights the tension between merchant checkout convenience and transaction security in Hong Kong's e-commerce ecosystem. With the HKMA explicitly stating merchants bear liability when they disable security measures, this could set a precedent for consumer protection in unauthorized credit card transactions. The case underscores the need for companies holding large customer databases to strengthen their cybersecurity infrastructure as digital payments become increasingly prevalent.